Tuesday, December 26, 2017

A Merry Christmas to us all; God bless us, every one!

Twas the Night before Christmas, when @realpresssecbot posted an image,
I was still browsing while Twitter glowed on my visage.
Merry Christmas it read, following dog whistles,
An itching it caused, as if sitting in thistles.

One of the very first responses that I saw to the original statement included a video mashup of former President and First Lady Obama saying "Merry Christmas." (Message me if it was you and I'll update this post to embed your tweet) Just in case the Republicans in my life and in my state sincerely believed the Statement by the President, I thought I should share this mashup video. I downloaded the file and shared it on Facebook from both my profile and my Page. The good thing about sharing from a Page is that you can boost the post.


I used my power to Boost the video into the Christmas Day news feeds of 35+ year old men in Maryland that like Donald Trump. This net will have caught some people that have told Facebook they are interested because they want to keep aware of what happens from the President, but it will mostly be older male Republicans. (AL exit polling showed that men still support DJT's messaging more than women and older more than younger)


Sadly, in a turn of events that will surprise no one, I did not have anyone thank me for removing their misconceptions. My personal profile post elicited one comment from a father of a high school acquaintance. He has been making a habit of posting sexist and racist comments on my posts so I was not surprised when a simple "Merry Christmas to all!" post was met with a "has been". Disappointed, but not surprised. I appreciate that he left off any racial slurs this time.


After nearly a day of running my post acquired 1,165 views with 452 of those making it at least 10 seconds in. (At 10 seconds the video has had "Merry Christmas" spoken 4 times.) The average view time was just 8 seconds, so the average viewer heard three "Merry Christmas"s. Two people shown the post chose to Hide All future posts from me which makes sense since Facebook generally works as an echo chamber and my targeted audience for this was Republicans. My Page is from when I ran for Congress as a Democrat.


The comments on the boosted post were what really got me though. Remember that this video was posted because the President of the United States has been regularly claiming that "Merry Christmas" was not welcome to be said before he was in office. If saying "Merry Christmas" is such a big deal to Republicans then a video of Barak Obama saying "Merry Christmas" on Christmas Day should be at worst ignored, right? That would be wrong. Over the course of today the post received two positive comments... "Merry Christmas", of course. The rest were pure vitriol and form quite a timeline through Christmas Day:

8:13 am

Greg Keeney: Fuck You

10:03 am

Chris Lunderman: You piece of shit

11:36 am

William Hidey: meme

William Hidey: meme

12:51 pm

Scott Carpenter: 1st and his pos

1:00 pm

Leon Issacs: Oh shut the hell up

3:13 pm

Charles Skinski: Fuck you no nothin politician

6:52 pm

Sean Lee Hughes: Fuck the prick and his family

7:10 pm

Chuck Snider: Fuck off

My reproduction here censored cases of incorrectly grouping either me or Obama into marginalized groups that we don't belong to. While the intended hate is clear it is neither a problem nor an insult to belong to the referenced groups. I have redacted the usage to keep from hurting readers by implying they are less if the labels apply to them.

I spent just under $10 to help establish common ground with my Republican neighbors over yesterday's holiday and considering that over 1,800 saw my post. Hopefully we can all agree that the phrase "Merry Christmas" was fully supported by the previous occupant of the White House. Some common ground has to be found for any meeting to be had, and a simple point like the President actively lies about easily disproved facts should be it.

To my Republican neighbors and family: do you want to continue to stand with Greg Keeney, Chris Lunderman, William Hidey, Scott Carpenter, Leon Issacs, Charles Skinski, Sean Lee Hughes, and Chuck Snider?

Saturday, December 16, 2017

Blocklisting dynamic paywalls on Google Chrome

Stop me if you have heard this one. When reading Twitter you find an interesting looking article linked. Before you outrage share it you decide to click through and read it.
It starts to load and suddenly you get this screen.

A dynamic paywall. Blast! Either you set up an account or you just outrage share based on the headline. I have a better solution! Type a magic url into the address bar:
chrome://settings/content/javascript


This brings up a simple looking settings page. You could toggle off the Allowed switch, but the modern Internet uses JavaScript for a lot of behavior. Your web browsing experience will suffer. Click the ADD button.

This brings up a popup text box "Add a site". Type in the fully qualified domain name: everything between the :// and the first /. www.nytimes.com is different than nytimes.com.


Once you hit ADD then you just go back to the page with the dynamic paywall. Hit REFRESH.

The page will load back up without the dynamic tracking and thus without the dynamic paywall.

This technique not only gets rid of the paywall this month, but forever.

Sunday, December 3, 2017

Introducing python module symcopy

Have you ever had a directory that you wished to copy the contents to another but you did not want to duplicate the file data? You use a symlink.

Now, what happens if you have migrated an entire directory to another drive and faked it with symlinks but then a Windows Update comes through and gets confused by your setup and refreshes your whole system?!

Oh look! Windows.old
I woke this morning to find that Windows Update had "fixed" my system. My symlinks were saved off in Windows.old and both Program Files directories were restored to fresh. Thanks, Windows.

To avoid reinstalling EVERYTHING, I decided to fix my problem from Windows rejecting my symlinks with... symlinks!
This would have been awful to type out and typing that many commands in an admin prompt can be a bit dangerous so I turned to my totally safe friend python. I needed to compare two directories, identify the items in the target that were not in the source, and create symlinks to them.
Don't worry about it being an image, I'm linking the Github.
The actual magic happens in that mklink function. I first implemented that as its own function because it was the first code I wrote this morning. Having it like that allowed me to easily test it before moving on. Once my problem was solved I decided to pip it up and share in case anyone (myself in the future...) has similar use cases, so the final version selects the correct command: ln or mklink.
I had never submitted code to pypi before so I prepared the package with the help of @mart0903.

And now: `pip install symcopy`
Demonstrated in docker: docker run --rm -it --entrypoint=/bin/bash python
PYPI: https://pypi.python.org/pypi/symcopy/
Source Code: https://github.com/SecsAndCyber/symcopy/

Saturday, December 2, 2017

Migrating %ProgramFiles% off of %SystemDrive%

Do not do this! I just had to do a fresh install of Windows 10 to finally get everything working again. Full disk format and install.

Yesterday I noticed a concerning state on my computer:
For a moment I wondered how I could have possibly filled that drive all the way up this fast. I just received this system in mid-October!

Oh yeah. I have games on here. Very, very large games. But I have that huge D. That should be able to relieve the pressure. So I set about copying both of my Program Files directories over.
 This took a while, as those two directories weigh in at 116 GB on disk for me right now. Once they were all copied I was left with another large problem: Windows uses stuff out of Program Files! There are open handles all over and so you cannot just move the directories. I needed to have access to my hard drives without Windows running. In the past (Windows XP days) this would have meant booting from an install media or booting up a Linux distro.

Thankfully, this is 2017 and I'm running Windows 10. There is now native support for rebooting into a diagnostic state that is not using your normal partitions. I followed the instructions documented by DigitalCitizen. Just pop open the Start menu and type Settings.

Click thru Update & Security and select Recovery.


 Once I was in the Advanced Startup screen I booted into Command Prompt.

For some reason my D: was mapped to C: and my normal C: was mapped to D:. It was a little weird. What I wanted to set up was NTFS junction points (symbolic links) at what my normal operating system thought was C:\Program Files and C:\Program Files (x86).

First, I made backup copies.
cd /d D:
move "\Program Files" "\_Program Files"
move "\Program Files (x86)" "\_Program Files (x86)"

And then I made the symbolic links... including with a bug!

mklink /D "\Program Files" "D:\InstalledSoftware\Program Files"
mklink /D "\Program Files (x86)" "D:\InstalledSoftware\Program Files"

Since the destination path is stored in the NTFS partition, I could point it at a location that didn't make any sense in the state I was at right there. Once I rebooted everything should work out fine.

I exited out to the Advanced Startup and allowed the system to continue into Windows 10. The first thing I noticed was that the system successfully booted. Once I logged in though I saw a bunch of my icons were broken. Just the shortcuts to 32 bit programs though. I compared the contents of D:\InstalledSoftware\Program Files (x86)\ and C:\Program Files (x86)\ and found that they didn't match. Strange. It looked more like C:\Program Files (x86)\ contained my 64 bit applications. Which it did.

A quick jaunt back to the Boot to Command Prompt let me fix it:
cd /d D:
rmdir "\Program Files (x86)"
mklink /D "\Program Files (x86)" "D:\InstalledSoftware\Program Files (x86)"

Excellent. On reboot all my icons looked find. Time to do a quick spot check of the file system before I delete the backups on C:
The file view in the C drive backup
The file view in C:\Program Files
Oh no! I broke all of the file system security settings by setting everything to be owned by Administrators. Is it even possible to restore a file to TrustedInstaller?! Turns out it is and it has been blogged about. And so I set about fixing a few directories.
Security Tab of File Properties on my directory
You cannot search for the TrustedInstaller account, but it is there.
Apply the changes down the whole tree.
Finally I had a directory restored! Yay! Now on to the next... 116 GB worth?! No. There had to be a way to script this. And so Powershell to the rescue.

Function Copy-ACL {
    Param (
        [string]$SrcPath,
        [string]$DestPath
    )
 
    $BaseACL = Get-ACL -LiteralPath $SrcPath
    Set-ACL -LiteralPath $DestPath -AclObject $BaseACL
 
    ForEach ($ChildItem in Get-ChildItem -LiteralPath $SrcPath -Recurse)
    {
        $DestItem = $ChildItem.FullName.replace($SrcPath, $DestPath)
        $SrcACL = Get-ACL -LiteralPath $ChildItem.FullName       
        if (Test-Path $DestItem)
        {
            Set-ACL -LiteralPath $DestItem -AclObject $SrcACL
        }     
    }
}
Now I could fix both trees.
Copy-ACL 'C:\_Program Files\' 'D:\InstalledSoftware\Program Files\'
Copy-ACL 'C:\_Program Files (x86)\' 'D:\InstalledSoftware\Program Files (x86)\'

Now... off to the races!
What is this? Oh, just rmdir /s /q %programfiles% ¯\_(ツ)_/¯
Thank you for coming on this journey with me. Next week I will blog about the total destruction I just made by massively modifying my workstation from 1am to 6am. I hope you enjoyed reading about it.
Free ALL the space!

Sunday, November 5, 2017

Finding World of Warcraft from Python

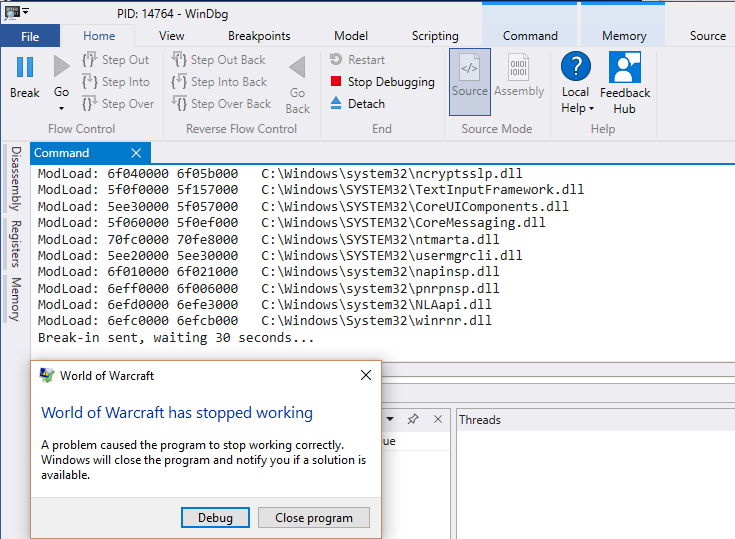
The typical way to locating a window programmatically is through the EnumWindows API and then identifying the hosting process through GetWindowThreadProcessId. Doing so right now, while I have World of Warcraft running is not returning the window that I'm looking for.
Notice that PID 14764
My first attempt was to enumerate through windows and use GetWindowThreadProcessId to lookup what process I was in. I set a global value to 14764 and let it run. No windows were detected.

Since it is obvious that there does exist a window I needed another approach. Next I set a loop running to print the window information every second for the return of GetForegroundWindow.
Window Text:     World of Warcraft
Class Name:      GxWindowClass
WindowThreadPID: 12336
 Great! I now know what to look for to discover the window. Lets just take a look at our processes when sorted by process id...
Hmmm, there is no 12336 process.
From Process Explorer I can use the Find Window's Process functionality. Right now though it is a mystery.

Update 1: I have downloaded the WinDbg Preview app and tried attaching to process 14764.
It didn't like that very much.
Update 2: I recorded the processes being created and then checked out my GetForegroundWindow information again. Not only is the alleged process ID not running, it was never started. I hope this does not need me to install a 43 GB game to a VM for kernel debugging.
Update 3: If attaching invasively caused the program to crash, lets see about noninvasive...
It seems that it said no.
The process refused the attach. Interesting...
Update 4: Debugging!
Crash prior to executable entrypoint
There is code running before the PE entrypoint gets to start which is not allowing me to debug it.

My first check was to use [sxe ld] to break on dll load, thinking that it might be pulling in a dependent Dll which is causing the crash from the DllEntryPoint. There is no module loads before the crash.

Next I will use the nearly magical Step to Address. I don't care where it steps to, I just want to see what the last function called before the crash is.

  • Start at the ntdll!LdrpDoDebuggerBreak breakpoint
  • Run the command [pa 1] which causes the debugger to step over until it reaches EIP=1, which will never happen. The last displayed instruction before the crash is our next path down.
  • After the step we see that LdrpInitializeProcess calls deeper. There is anti-debugging code abusing TLS initialization.
    • ntdll!LdrpInitializeProcess+0x1b42:
      76fdf7a5 call    ntdll!LdrpCallTlsInitializers
  • This process will be repeated with breakpoints on each call deeper.
    • bp ntdll!LdrpCallTlsInitializers
    • ntdll!LdrpCallTlsInitializers+0x5731d:
      77003a92 call    ntdll!LdrpCallInitRoutine
    • bp ntdll!LdrpCallTlsInitializers "bp ntdll!LdrpCallInitRoutine"
    • ntdll!LdrpCallInitRoutine+0x7a:
      76faf30a call    ntdll!LdrxCallInitRoutine
    • ntdll!LdrxCallInitRoutine+0x13
      76fe1cd3 call    dword ptr [ebp+8]    ss:002b:Wow+0x3fd0
    • ntdll!LdrxCallInitRoutine+0x13
      76fe1cd3 call    dword ptr [ebp+8]    ss:002b:Wow+0x7030
  • Now I see where the code execution is beginning. This is where I would normally switch to static analysis, but I have not fully set up my home system since the upgrade a few weeks ago. No IDA Pro today.
  • Restart again and jump directly to that spot. Remember that `g <address>` or `bp <address>` both patch memory with software breakpoints and I would rather not do so.
    • bp ntdll!LdrxCallInitRoutine "ba e 1 Wow+0x7030;gc"
  • If OMG verbosity is your thing then you can use the Trace to Address to run to the crash and record everything that happens. This is a very slow process!
    • ta 1
  • I ran the above command and then wrote the above text. It still has not gotten to the crash yet.
    • I bailed out
  • Instead I am switching to the [pa 1] trick again.
    • Wow+0x703f:
      call    Wow+0x7120
  • This next function has a lot of instructions. 
    • It has no calls, so [pa 1] and [ta 1] are displaying the same behavior... too damn slow
    • As my screenshot though shows, there are first chance exceptions being observed. 
      • I want to see all first chances... [sxe *]
    • Unknown exception - code c0000096 (first chance)
      Wow+0x186c8:
      012586c8 hlt
    • Hlt will do it. That is a privileged instruction.
  • And I'm going to stop with this rabbit hole now. The one thing to note is that the crash if different if I slow down execution, so there are multiple anti-analysis techniques in place.
  • This route is turning up fruitless as to why can't I properly detect the window as expected.

Last update! Conclusion!

Accessibility code for the win.
def GetRealOwnerProcessId( hwnd ):
    """
        This leverages the 'Active Accessibility User Interface Services Client Function' GetProcessHandleFromHwnd
        It avoids whatever is the problem that keeps GetWindowThreadProcessId from working as expected.
    """
    PH_PID = -1
    ProcHandle = GetProcessHandleFromHwnd(hwnd)
    if ValidHandle(ProcHandle):
        PH_PID = GetProcessId(ProcHandle)
    CloseHandle(ProcHandle)
    return PH_PID
I can now successfully locate the real World of Warcraft process by enumerating the windows.

Sunday, October 29, 2017

To be clear: White Pride is just racism

I saw this tweet again today and want to expand on it.

Once again, louder for those in the back.
"White" is defined by the experiences it doesn't experience.

It has reminded me of an image that was being distributed on Facebook: 
I can see apparent contradiction that is being demonstrated here. There is one significant thing missing from that appearance: context. Context is everything and is all too often stripped from anything which addresses the legacy of white supremacy.

Asia is a place. The people from there are Asians. Europe is a place, and it is home to Europeans. Both tend to associate more strongly with their national background then the continental one anyway. Additionally, America is two places (three or four even depending on regional labels) and as such an entire hemisphere of people are Americans. Which makes the dog whistle "Real Americans" all that much more incorrect and ignorant.

In the past Africans had their cultures, families, and even their names stripped and beaten from them. All they were left with was their blackness and then punished for that. Descendants did not know where their ancestors were from, as families were split apart and sold to different sections of the continent. Literacy was banned and teaching it was punishable after it enabled revolts. All that they had left was their blackness, which was also their curse. That legacy has held on, black people isolated and punished for their blackness through explicit laws and de facto abuse. Black is what is left and a shared culture derived from it.

White people never had their life and culture stripped away. There is no shared experience for white people to draw on. Racists are proud to be white because it means not having lived the trials of others.

German heritage is celebrated. Irish heritage is celebrated. French, Welsh, Scottish, Russian, Scandinavian, Italian, Swiss, etc. There is no united White culture.

Consider the symbols used to support White Pride: Confederate and Nazi iconography. One rooted explicitly in preventing black equality and promoting white supremacy. One which committed mass genocide to exterminate the "other" based on racial, sexual, religious, and ideological lines.

Contrast this to the often cited, by white racists, Black Power movement with its easily recognizable raised fist used by the Black Panther Party. Rather than being based on subjugating and exterminating people, the first "means life and liberty being fought for and a greeting of solidarity with the democratic peoples of the world." (Letters from Spanish Civil War, 1938) A raised fist is often displayed as a signal of strength and solidarity against oppression, which has been the default state of black USians for the majority of the European colonization of North America and then the United States of America.

Five hundred years of oppression by white people in North America has made Black have its own culture independent of religion and nationality. It is not racist for that culture to be owned and celebrated. It is a sign of strength to succeed and to even flourish in such an environment. That strength, a strength that white USians will never experience or be able to fully grasp, is something worth being proud of.


Friday, October 27, 2017

Harassment: Should you ask that question on your mind?

Early this month a tweet sized anecdote was shared concerning a recent interaction with TSA. While traveling, the author smiled at an agent and was rewarded with a sexually loaded request for personal information. The resulting feedback from the Internet was... mixed. I used the moment to support the author's concern because of its intersection between abusive law enforcement and women's safety.

Unbeknownst to me at the time, the original author has well over half a million followers. Since "woman with safety concerns" seems to be a favorite of toxic Internet trolls, the thread in question was visited with massive amounts of vitriol. I have not read through the thousands of replies to the original post, nor tracked down the thousands of retweet quotes, so I can only discuss the slice of the conversation after I posted. There is no amount of money that I would accept to have to read the full mentions of the author from that day though.
Among my replies and mentions there seems to be basically three themes: how can men meet women, who had power during the original interaction, and personal attacks against me. While the personal attacks were uncomfortable, I have no useful discussion for them. To quote Wil Wheaton... "Don't be a dick." Suffering through such attacks for supporting a woman online still doesn't provide me the perspective of the suffering required to be a woman online. Listen to them, read their accounts, and believe them. We can be better.

At 140 characters, or even at the future 280 characters, there is not much room for nuance in a tweet. That was discussed a bit in my replies and one user requested I expand on it. This is my wider post to add the nuanced discussion that was condensed into my Twitter post.

Questions that need to be asked

Positions of power exist because our society utilizes hierarchy and specialization to function as well as variations among people. All three of these points create fluid power dynamics between actors which change based on the context of the moment. A smaller, soft spoken man might be normally quite amicable, but intimidating and threatening when out with his three large bruiser appearing pals. Mobster depictions in media are great examples of this dynamic. Entrepreneurs are have a lot of power in their role as employer, even if they come across as unimposing in other relationships. Badges and uniforms tend to carry significant influence and discretionary impact.
Hierarchy and specialization necessarily brings about communication that is required by the roles and situations that they generate. As such, these roles generate questions that must be asked, even if they might seem intrusive and involve personal information. Recruiters and hiring managers have to confirm that applicants will be able to complete an I-9 form to demonstrate legal work status. For clearance jobs they must confirm US citizenship. Nurses will have to ask about medical history and family medical history. Police, when in the course of an investigation, will need to ask questions to advance the investigation. Questions dictated by law or by context are always appropriate: they can and should be asked.

Small talk

Small talk consists of light discussions that fill otherwise silent time typically does not involve soliciting personal information, interrupting activity, and can be between speakers of any level of familiarity. Discussions of drink choices, current weather, and not intrusive compliments or sourcing queries about clothing are rarely inappropriate, when short, nondisruptive, and amicable. "I like your shoes. Where did you get them?" keeps the conversation light. Further inquiry, like which specific building, whether it is in walking distance of their house or job, or sexual comments of where they could leave the shoes push the conversation into a place where the target is likely to feel pressured or threatened.

How might a power imbalance be detected?

Obviously this does not apply to you, but place yourself into the mind of the target and ask "What could they do with this information?" and "What could a vindictive person do to retaliate?" No matter who you are, information like where they keep security backups, like a spare house key, is a potential threat. Where their children are at when no family members are near is a potential threat. (Consider the movie Blow and when the pilot has to turn over information about his children) It really should go without saying, but making yourself a threat creates a power imbalance. Unless necessitated by the situation and context, do not solicit information that can make you a threat.
Moving away from how an information disclosure might make you a threat, we need to address how you may already be a threat. As a reminder, people cannot give free and open consent (to anything) under threat, which creates duress. Requests for favors, sexual advances, contract acceptance, or the like all need to take place while all parties are freely consenting. Any situation where you are requiring the other party to provide acceptance or rejection might result in you being rejected. You are a threat if it is possible to retaliate if rejected.

Retaliations that you would never perform

If you are…then you pose a threat of...
Physically imposing and there are not witnessesimmediate assault.
A stranger on the streetfollowing and delayed assault.
A local law enforcement officerabuse from behind the badge, targeted investigation, or sexual assault ("frisk" or "cavity search").
A TSA agentdetainment, arrest, and sexual assault ("frisk" or "cavity search").
An educatorderailing their educational goals.
A mentorderailing their professional goals.
A supervisorabuse through scheduling: spiteful shifts or lack of shifts, or even termination.
Well connected in their fieldblacklisting and other forms of derailing their goals.

Conclusion

Harassment, in general and sexual harassment specifically, can come in many forms and so this discussion alone will not keep you from committing it. This discussion will, though, help recognize interactions that are always harassment. Do not ask favors, including and especially related to sex, from a position of power. Just don’t do it, because the other party cannot provide free and open consent to accept. If there are potential repercussions to rejection, do not solicit it. That is harassment at best.

PS...
@LandryRobandry, please DM me to request my mailing address.